Passkeys in the AI Era: A Developer’s Practical Guide
A practical guide for developers explaining how passkeys, WebAuthn, and FIDO2 provide phishing-resistant public-key authentication to defend applications against AI-driven threats
Author
Shalimar Mehra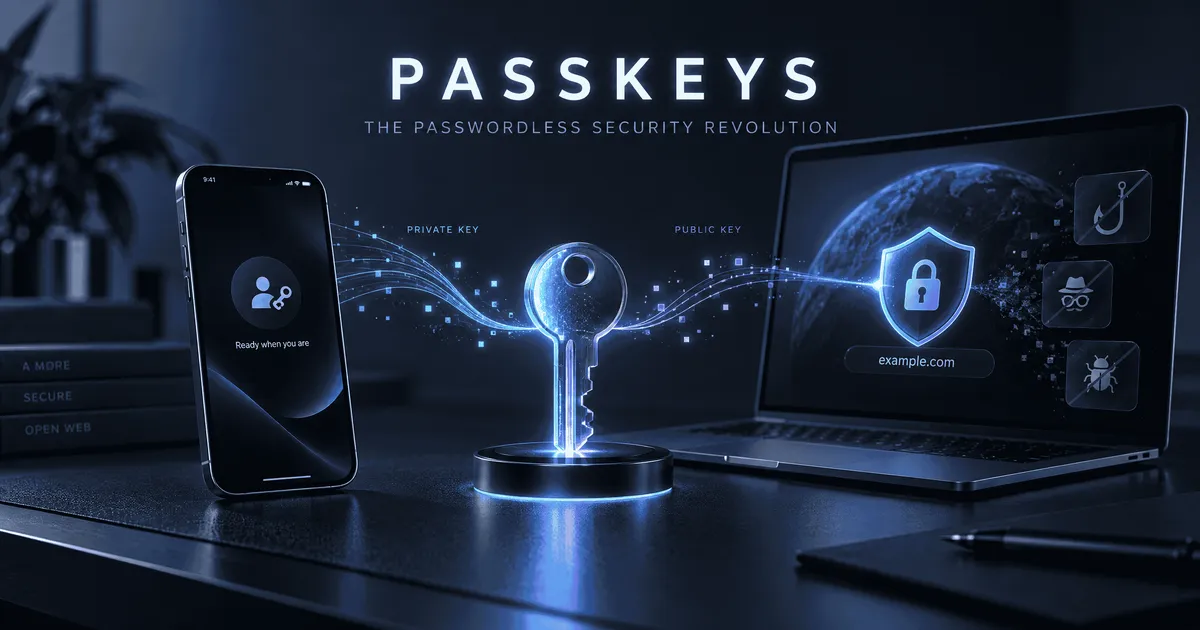
Introduction
Did you know that 80% of all data breaches still stem from traditional typed passwords, and automated AI phishing bots can fool even seasoned software engineers 47% of the time? Relying on shared text secrets typed into web forms is no longer just risky—it is obsolete. Enter passkeys, the cryptographic revolution reshaping how we secure the modern web.
By the end of this lesson, you will be able to:
Compare the underlying cryptographic architecture of passkeys against traditional passwords, TOTP 2FA, and hardware tokens.
Explain the step-by-step WebAuthn and FIDO2 challenge-response flow during registration and authentication.
Analyze the operational differences between synced, device-bound, and cross-device passkey implementations.
Evaluate developer verification steps and account recovery strategies to prevent fallback vulnerabilities.
Distinguish between authentication and authorization when protecting systems against AI-driven threats.
The Fall of Passwords and the Rise of Asymmetric Security
Imagine you have a master key to your front door. For decades, the web operated on a simple but flawed model: you and a remote server both kept exact copies of that key (or a hashed version of it). If a thief breaks into the server's vault, they steal everyone's key. Attackers run offline dictionary scripts, leverage credential stuffing across reused passwords, and trick users into typing their keys onto fake phishing sites. To make matters worse, generative AI tools have fueled a staggering 3,000% spike in AI-powered phishing attacks, rendering traditional shared secrets fundamentally broken.
Passkeys flip this model completely on its head using asymmetric public-key cryptography. Instead of sharing a secret, your device acts like a key generator that creates a unique pair of cryptographic keys for every single website:
The Private Key: Stored permanently and securely inside your device's protected hardware enclave—such as an Apple Secure Enclave, Android TEE (Trusted Execution Environment), or Windows TPM (Trusted Platform Module)—or within an end-to-end encrypted password manager. It never leaves your device.
The Public Key: Sent directly to the application server (known in technical specs as the Relying Party). It is a non-sensitive public artifact used solely to verify cryptographic signatures.
When comparing authentication models, passkeys provide a massive upgrade in both security and user experience:
Passwords: Rely on shared secrets. High server breach exposure and zero phishing resistance. Average sign-in takes 31.2 seconds with a 63% success rate.
Password + SMS / TOTP 2FA: Adds protection, but SMS is vulnerable to SIM-swapping, and TOTP can be captured by Adversary-in-the-Middle (AitM) phishing proxies.
Hardware Security Keys (e.g., YubiKeys): Offer absolute phishing resistance via hardware-bound keys, but lack automated cloud backup. Sign-in takes ~8.5 seconds.
Passkeys (FIDO2 / WebAuthn): Provide absolute phishing resistance alongside native OS integration. Sign-in takes 8.5 seconds with a 93% success rate.
A common worry among users is biometric privacy: Does the website get my fingerprint or Face ID? The short answer is no. Through the Local Unlock Guarantee, biometric sensors act purely as local authorization switches. Face ID or fingerprint scans take place entirely inside your device's secure chip to unlock the local key container. The website server receives only a signed mathematical proof that local verification succeeded—never your biometric data or PIN.
Also Read this: Googlebook AI Laptop Guide: Specs, Gemini Features & Android Integration
Under the Hood: FIDO2, WebAuthn, and the Cryptographic Handshake
How do passkeys actually execute a passwordless login in practice? Under the hood, passkeys rely on the FIDO2 framework, which brings together two vital open standards:
WebAuthn (Web Authentication API): The browser-level JavaScript API that web applications use to request credential creation and authentication signatures.
CTAP (Client to Authenticator Protocol): The low-level protocol enabling your browser to communicate with the hardware enclave or security vault.
Authentication operates as an asymmetric challenge-response ceremony. Think of it as a digital handshake where the server issues a unique puzzle, and only your private key can produce the exact mathematical signature to solve it.
Here is how the two primary flows work:
Registration Ceremony: The application server generates a cryptographically random challenge string and sends it to the browser. The authenticator creates a fresh 256-bit elliptic curve key pair (e.g., ES256 / Ed25519) scoped strictly to the site's origin domain (the Relying Party ID or rpId). The private key is saved locally, while the public key and a unique credential ID are returned to the server.
Sign-In Ceremony: When you return, the server issues a new ephemeral challenge. The browser invokes
navigator.credentials.get(), prompting your local OS for biometric verification. Once validated, the hardware enclave signs the challenge buffer with the stored private key. The server uses its registered public key to verify the signature and log you in.
Not all passkeys are stored or transported the same way. The FIDO framework defines three distinct operational models:
Synced Passkeys (Multi-Device Credentials): Stored inside end-to-end encrypted cloud vaults like iCloud Keychain, Google Password Manager, 1Password, or Bitwarden. If you drop your phone in the ocean, logging into your cloud provider account on a new phone automatically restores all your passkeys.
Device-Bound Passkeys (Single-Device Credentials): Generated inside dedicated hardware tokens like YubiKeys or enterprise TPM modules. The private key is non-exportable and physically trapped on that chip.
Cross-Device Passkeys (Hybrid Transport / caBLE): Want to log into a desktop browser using your phone? The desktop displays a dynamic QR code. Scanning it with your phone opens an encrypted WebSocket tunnel accompanied by a Bluetooth Low Energy (BLE) proximity check. The BLE check ensures both devices are in the same room, effectively stopping remote relay attacks in their tracks.Developer Blueprint: Implementation, Verification, and Recovery Architectures
For developers, implementing WebAuthn requires precise coordination between browser APIs and backend verification logic. On the front end, initiating authentication requires calling navigator.credentials.get() with mediation: 'conditional' to enable seamless WebAuthn Conditional UI and browser autofill.
Once the front end receives the credential response, the backend server must execute strict mathematical verification before authenticating the session:
Parse clientDataJSON : Ensure the event type matches
webauthn.getorwebauthn.create, verify the challenge matches your issued ephemeral server challenge, and strictly confirm the origin matches your expected domain name.Inspect authenticatorData : Verify that the SHA-256 hash of the
rpIdmatches your domain. Check essential bitwise flags: User Presence (UP, Bit 0) must be 1, and if required, User Verification (UV, Bit 2) must also be 1.Validate Signature: Verify the assertion signature over the concatenated binary buffer of
authenticatorDataandclientDataHashusing the raw stored public key.Store Metadata: Store raw COSE-encoded public key bytes, credential ID, signature counter, and transport flags in your database.
Crucial Warning: Never hand-roll custom WebAuthn cryptographic parsing! WebAuthn responses involve complex CBOR (Concise Binary Object Representation) maps, COSE key formats, and ASN.1 DER signature structures. Flaws in manual bitwise parsing lead to severe authentication bypass vulnerabilities. Always rely on audited, maintained libraries like @simplewebauthn/server (Node.js), py_webauthn (Python), webauthn4j (Java), or go-webauthn (Go).
The biggest architectural landmine when deploying passkeys is account recovery. If a platform deploys phishing-resistant passkeys but permits account recovery via plain email links or unencrypted SMS OTPs, the overall security of the system degrades to the strength of that weak recovery path. Attackers will simply trigger the recovery flow to bypass the passkey entirely!
To build a resilient passkey architecture:
Support multiple passkeys per account (e.g., phone, laptop, hardware key) without overwriting existing entries.
Provide clear management UI for users to inspect metadata and revoke lost keys.
Leverage the WebAuthn Level 3 Signals API (
PublicKeyCredential.signalUnknownCredential) to notify browser credential managers when a key has been revoked on the server.Require high-entropy offline recovery codes or out-of-band administrative verifications for account recovery.
Adopt a phased rollout: offer passkeys as an optional method, promote them via conditional UI, keep fallbacks temporary, and track key health metrics like passkey creation rate and login success rate (aiming for ~93%).
Defending Against AI Attacks and The Future of Identity
Why are passkeys becoming mandatory in the age of artificial intelligence? Modern generative AI models allow bad actors to produce context-aware phishing emails, flawless voice clones, and real-time deepfakes at near-zero marginal cost. Security awareness training alone can no longer protect human users from being deceived.
Passkeys neutralize this threat through cryptographic domain binding by design. Because key generation and signing ceremonies are strictly bound to the application's domain origin (rpId) verified by the browser engine itself, a user fooled by a hyper-realistic deepfake into visiting fake-bank.com cannot leak credentials for bank.com. The browser queries the authenticator for fake-bank.com, finds no matching private key, and refuses to sign the challenge. Phishing is rendered mathematically impossible.
As we look toward an ecosystem driven by autonomous AI agents writing code, deploying infrastructure, and invoking APIs, understanding the boundary of passkey protection is vital:
Authentication ("Who is acting?"): Passkeys excel at verifying the primary human identity or initiating entity during sign-in through local hardware validation.
Authorization ("What can they do?"): Passkeys do not manage API token scoping, defend against post-login session hijacking, or prevent prompt injection attacks on downstream AI agents.
To build robust AI-era applications, developers must pair passkey authentication with strict least-privilege authorization frameworks, short-lived session tokens, and continuous behavioral monitoring.
Summary
Passkeys revolutionize web security by replacing vulnerable, typed shared secrets with asymmetric public-key cryptography bound to specific web domains. By leveraging local hardware enclaves and WebAuthn standards, passkeys eliminate phishing, protect server databases from leaks, and streamline sign-in into a single 8.5-second biometric gesture.
Key Takeaways:
Phishing Immunity: Passkeys bind private keys to domain origins (
rpId), completely rendering AI phishing, deepfakes, and server database leaks ineffective.MFA in One Gesture: Unlocking a passkey combines possession ("something you have") and inherence ("something you are") in a single biometric scan or PIN entry.
Biometric Privacy: Facial, fingerprint, and PIN data stay inside local hardware enclaves; site servers receive only signed mathematical proofs.
Architectural Rigor: Protect against fallback vulnerabilities by using high-entropy recovery codes, supporting multiple enrolled keys per account, and leveraging standard WebAuthn libraries like
@simplewebauthn/server.Phased Deployment: Roll out passkeys progressively with conditional autofill, while monitoring adoption metrics like creation rate and login success rate (~93%).
Also Read this: Googlebook AI Laptop Guide: Specs, Gemini Features & Android Integration
Community Discussion
Loading comments...
Join the Conversation
Log in to post your thoughts, ask questions, and engage with authors and developers.
Log in to Comment